
Threat Hunting
Proactively hunt hidden threats with threat intelligence and behavioral analytics instead of waiting for alerts.
Overview
Most intrusions dwell for weeks before discovery. Attackers use legitimate tools for lateral movement and built-in commands for persistence, leaving traces scattered across endpoint, network, cloud and email logs — while analysts face hundreds of alerts a day and the one that matters is easily buried. Retaining logs for compliance is not the same as using them.
Threat hunting works from hypothesis: using intelligence and the ATT&CK framework to ask where an intruder would leave traces, then testing that hypothesis against telemetry. Check Point XDR consolidates network, endpoint, cloud, email and identity signals, automatically correlating seemingly unrelated events into a complete attack chain and timeline, with built-in hunting playbooks that make investigations repeatable.
For lean teams this combines with managed detection and response for around-the-clock coverage. Effectiveness should be measured by ATT&CK technique coverage, mean time to detect and confirmed-threat rate — not alert volume. GSAFE helps establish hunting operations, detection rules and regular exercises.
Key capabilities
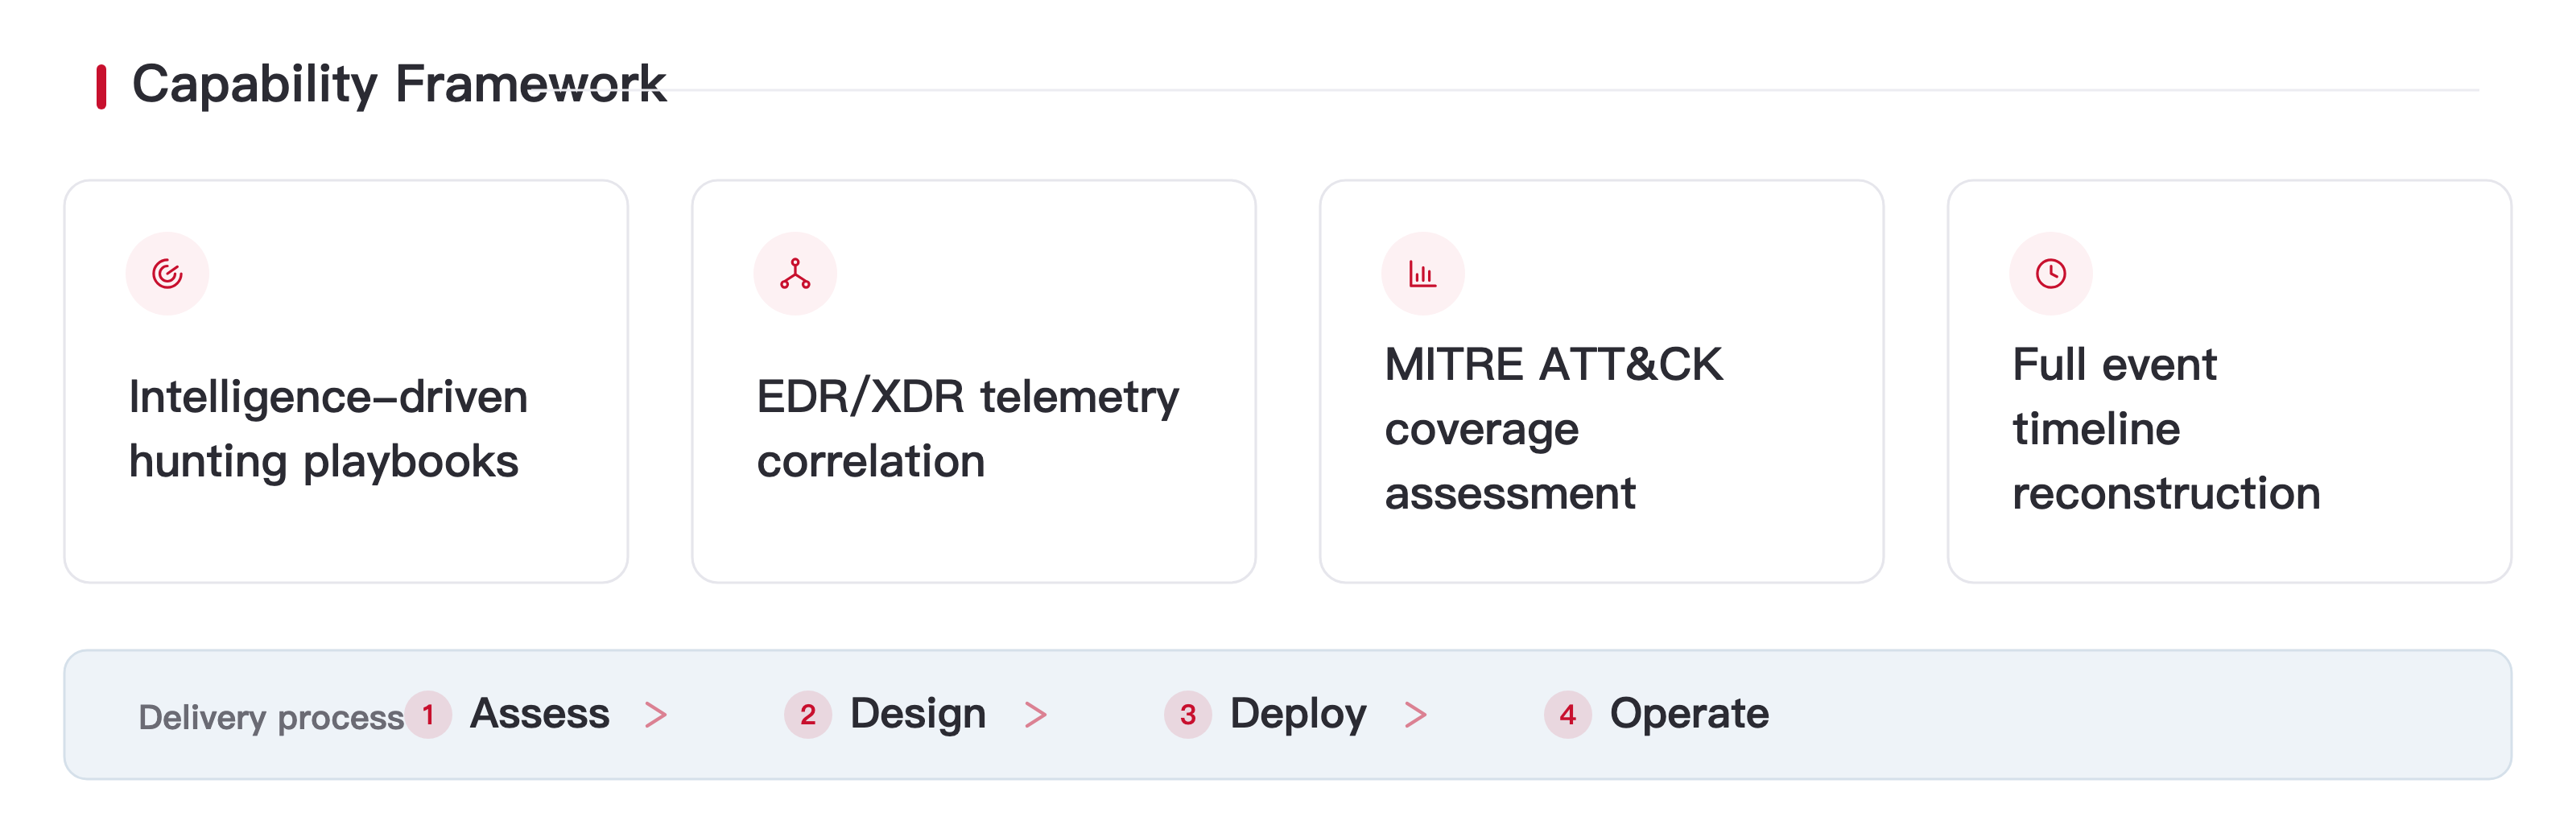
- Intelligence-driven hunting playbooks
- EDR / XDR telemetry correlation
- MITRE ATT&CK coverage assessment
- Full event timeline reconstruction