
Developer Security & Operations
Embed security across CI/CD, from infrastructure-as-code scanning to image and cloud configuration baselines.
Overview
Cloud-native delivery compresses deployment from weeks to minutes and moves risk at the same speed: an over-permissive bucket policy, a committed access key or a vulnerable base image can expose an environment instantly, while quarterly penetration tests cannot keep pace with daily releases.
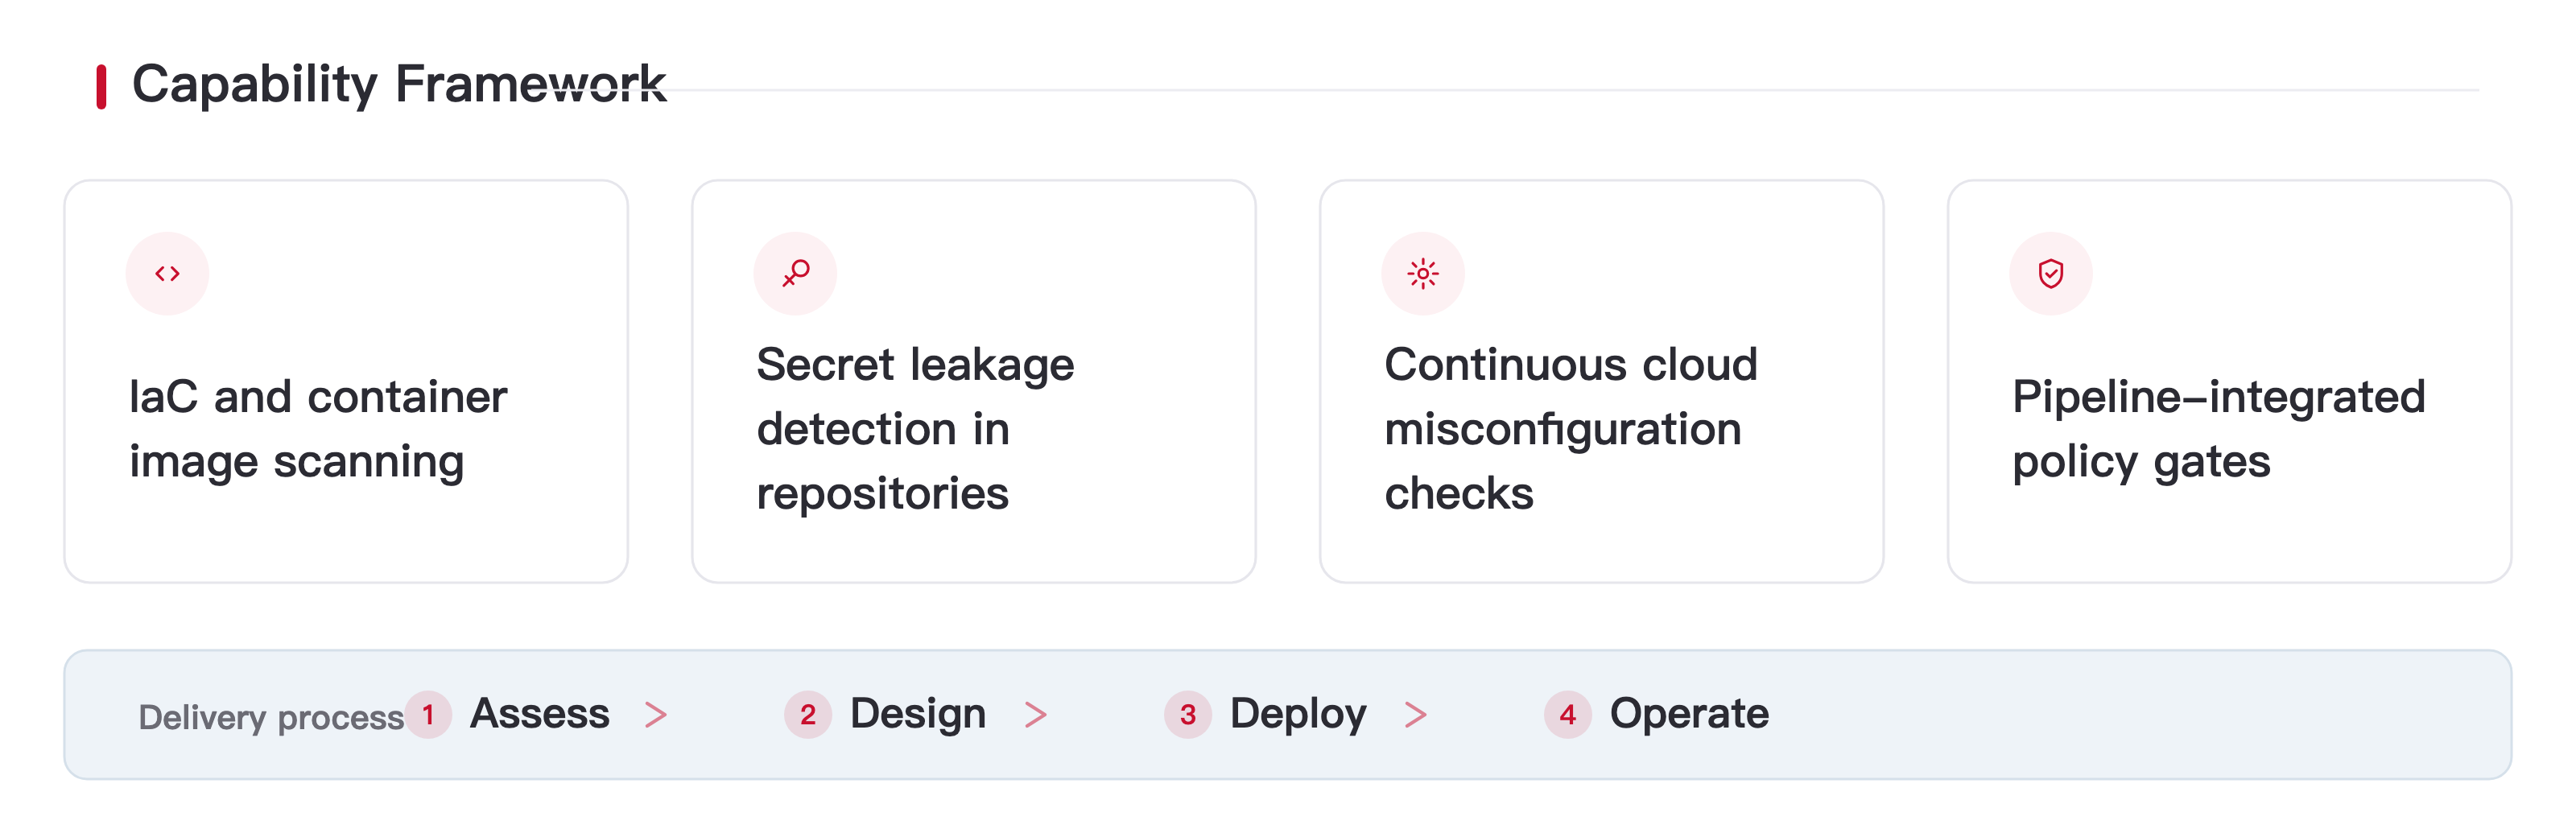
Check Point shifts checks into the pipeline — pre-commit IaC scanning for Terraform and CloudFormation, container image vulnerability and malware scanning, continuous secret-leak detection in repositories, and policy-as-code gates that block merges or deployments that violate cloud baselines.
Runtime protection closes the loop: CNAPP continuously assesses posture, cloud-native firewalls and WAF protect live assets, and runtime sensors flag anomalous processes and lateral movement, all traceable back to the responsible commit. GSAFE helps map existing CI/CD tooling and define gate thresholds and exception workflows.
Key capabilities
- IaC and container image scanning
- Secret leakage detection in repositories
- Continuous cloud misconfiguration checks
- Pipeline-integrated policy gates