
CTEM (Continuous Threat Exposure Management)
Continuously discover, assess and prioritize exposure so attacker-view risk becomes an actionable remediation list.
Overview
Attack surface expands faster than asset management: internet-facing IPs and ports, forgotten test environments, shadow APIs, publicly readable cloud storage, third-party components and credentials leaked on external platforms form the world attackers actually see. What defenders see is usually a scanner list — tens of thousands of findings ranked by CVSS and barely related to where an attacker will enter tomorrow.
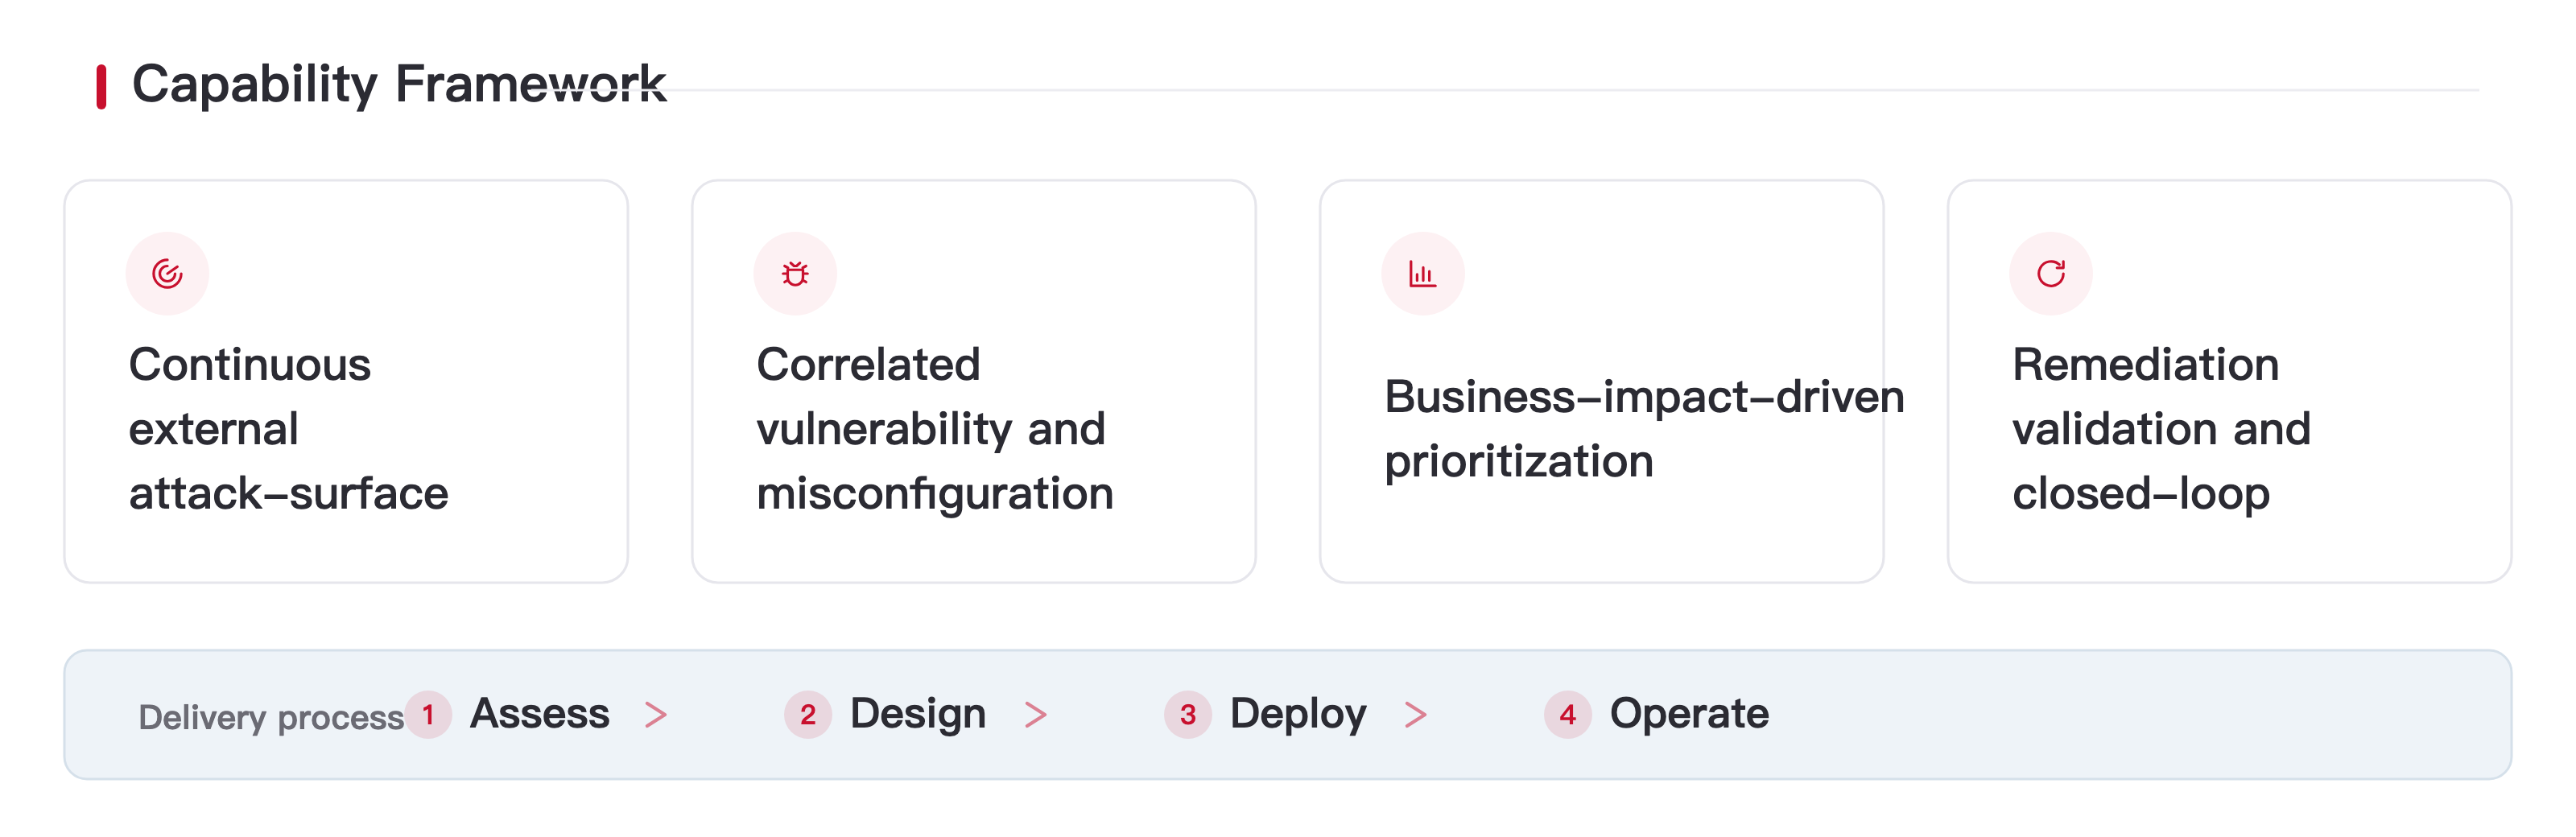
Continuous Threat Exposure Management assesses from the attacker's viewpoint: continuously discover the organisation's external assets, including unknown and shadow assets, and confirm ownership; correlate vulnerabilities, misconfigurations, identity and data exposure to identify combinations that are genuinely exploitable; validate exploitable paths rather than inferring from scanner output; then prioritise remediation by business impact and verify fixes to close the loop.
The value is freeing teams from an endless vulnerability list to focus on the few paths that will actually be used. It requires asset, vulnerability, configuration and intelligence data to be connected, plus business involvement in ownership and impact. GSAFE supports exposure inventory, attack-path analysis and remediation prioritisation.
Key capabilities
- Continuous external attack-surface discovery
- Correlated vulnerability and misconfiguration risk
- Business-impact-driven prioritization
- Remediation validation and closed-loop tracking