
Compliance
Map requirements such as MLPS 2.0, ISO 27001 and GDPR onto enforceable policies and audit reports.
Overview
Regulatory frameworks and China's Multi-Level Protection Scheme (MLPS 2.0) turn compliance into continuous evidence rather than a one-off audit. In practice configurations drift, blades are left disabled and temporary policy exceptions stay permanent — so the compliant state quietly expires.
Check Point Security Compliance uses 300+ security best practices as a baseline, continuously monitoring gateways, software blades, policies and configuration settings, translating thousands of regulatory requirements into verifiable technical controls. Deviations trigger real-time alerts with remediation guidance.
Results integrate with SmartEvent for management and auditor-ready reporting, turning “are we compliant” into measurable, traceable data on the same management plane as firewalls, endpoints and cloud. GSAFE supports baseline review, gap analysis, remediation and audit preparation.
Key capabilities
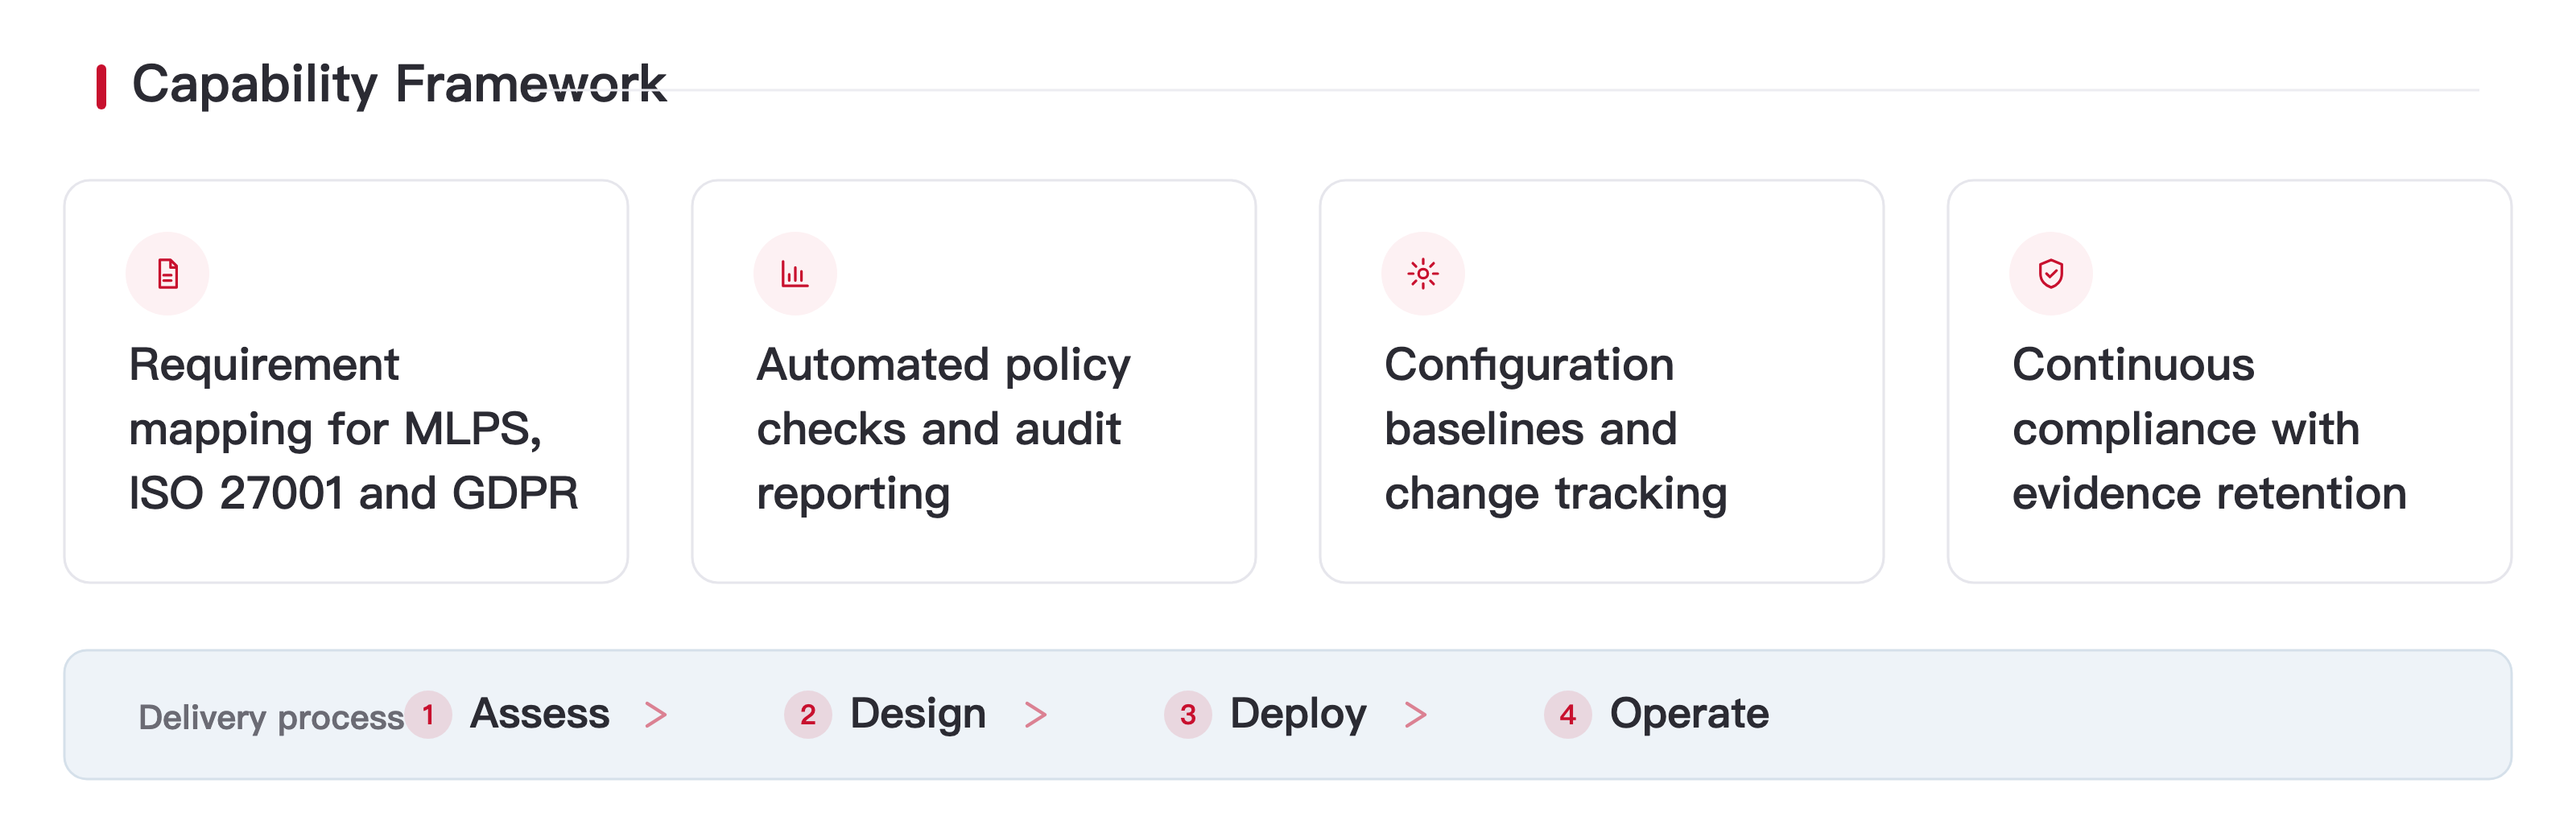
- Requirement mapping for MLPS, ISO 27001 and GDPR
- Automated policy checks and audit reporting
- Configuration baselines and change tracking
- Continuous compliance with evidence retention