
AI Security
Governance for LLM applications and AI workloads, covering usage compliance, prompt-injection defense and AI asset visibility.
Overview
AI adoption has outpaced security controls. Employees paste contracts and customer data into public models, creating unmanaged shadow AI; customer-facing applications introduce prompt injection and jailbreaks; and agents that call tools, read files and execute actions turn “saying the wrong thing” into “doing the wrong thing”.
Check Point covers three layers with one defence plane: workforce controls discover AI use across browsers, SaaS and copilots with sensitive-paste detection and DLP; application controls block prompt injection, jailbreaks and exfiltration inline with low latency; agent controls restrict tool use and privileges, block unsafe autonomy and mitigate looping denial-of-service.
AI red teaming continuously tests models and agents against real adversarial techniques mapped to OWASP risks. The operating model is discover, protect, govern — visibility first, runtime enforcement second, unified policy and audit last. GSAFE supports AI asset inventory, risk tiering and guardrail design.
Key capabilities
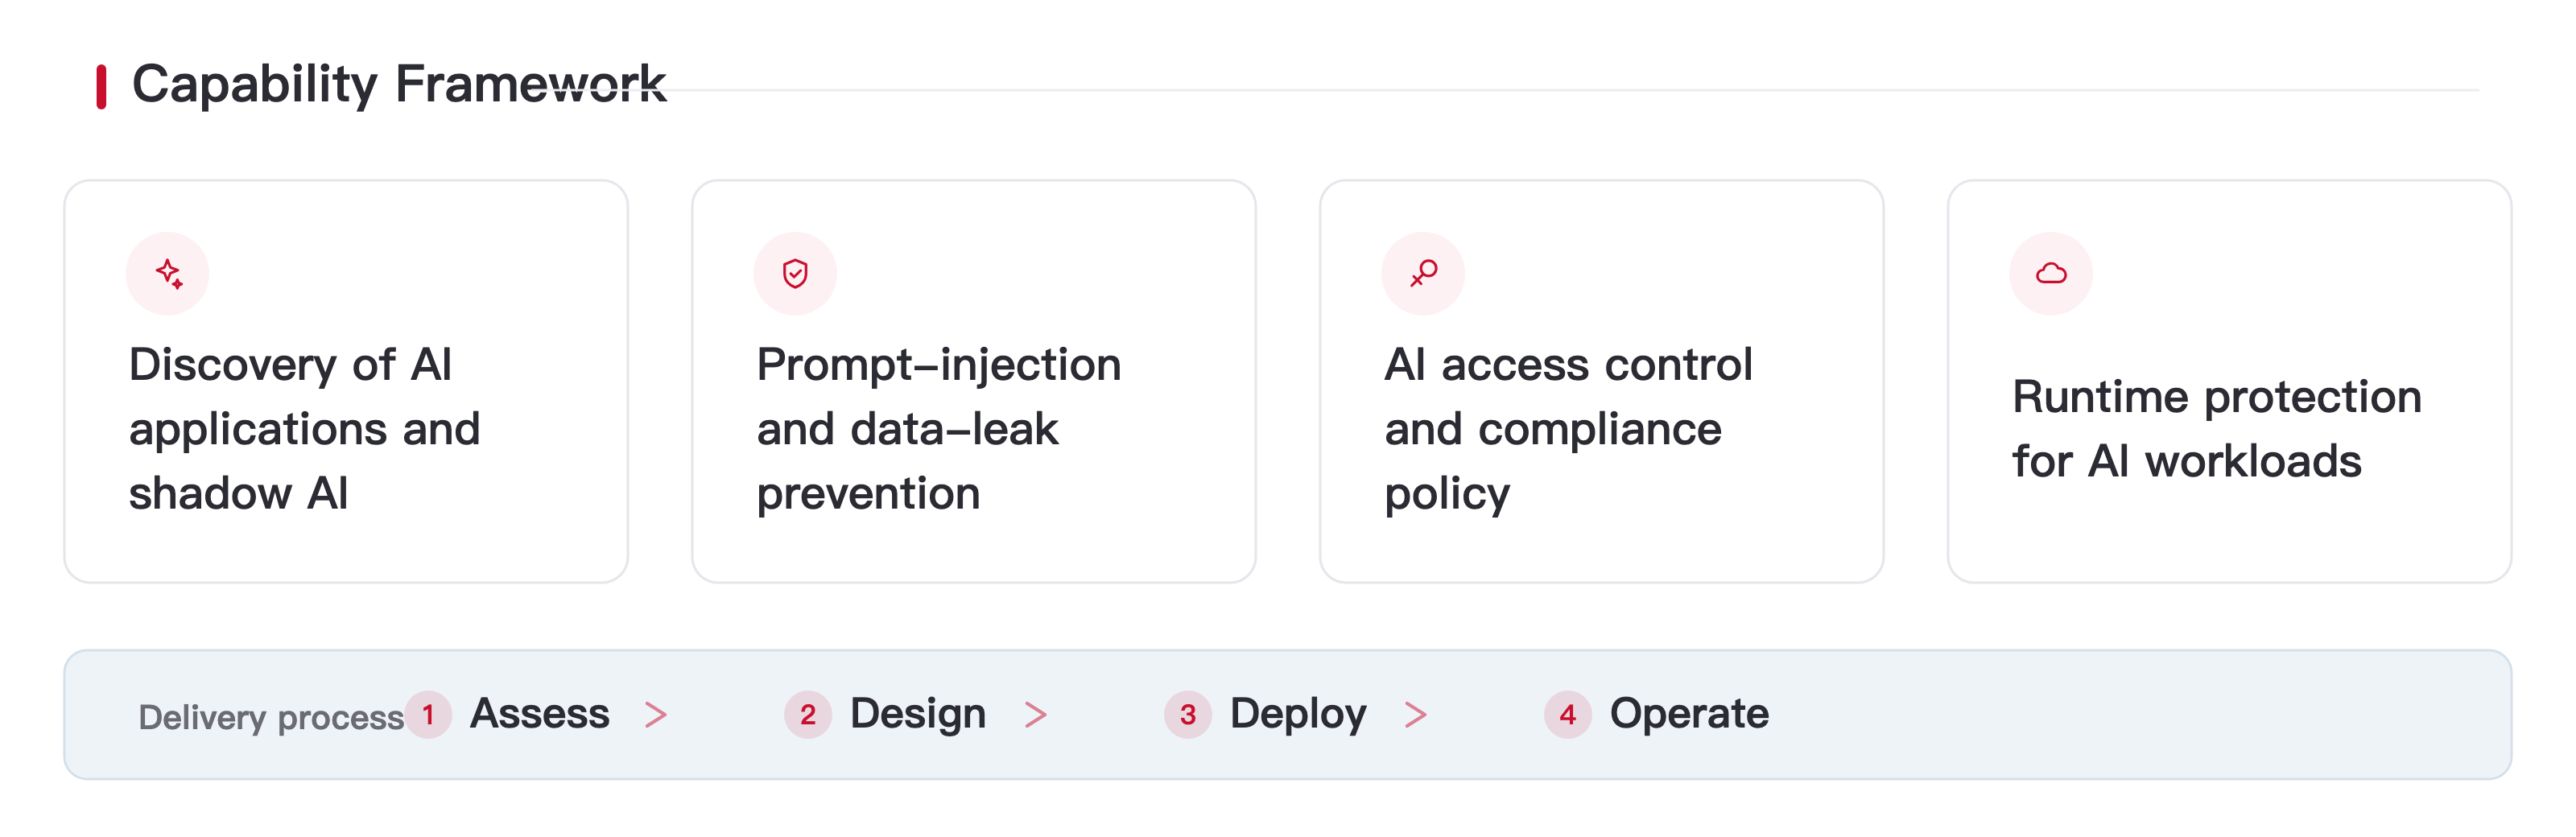
- Discovery of AI applications and shadow AI
- Prompt-injection and data-leak prevention
- AI access control and compliance policy
- Runtime protection for AI workloads