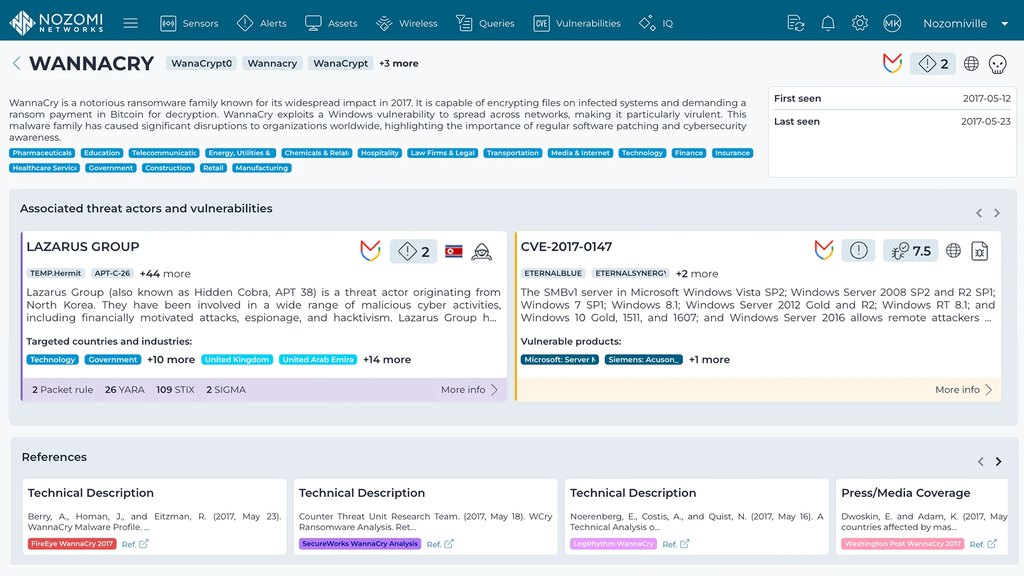
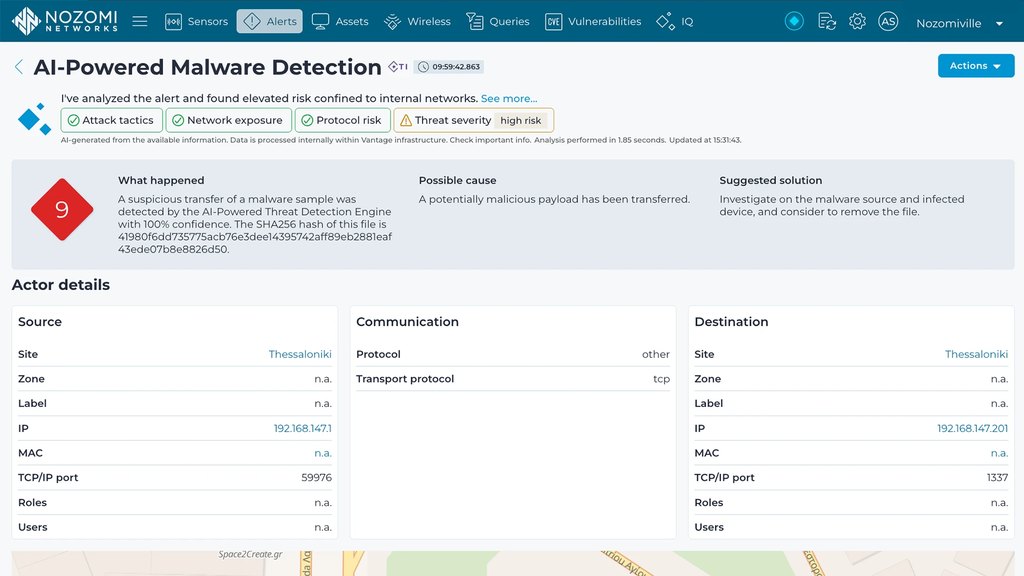
Nozomi Threat Intelligence – Actionable OT/IoT Threat Intel
Comprehensive Insights into OT & IoT Threat Actor Behaviors
Nozomi Networks Labs analyzes more than a dozen public and private sources plus anonymized customer telemetry to produce actionable OT/IoT threat intelligence, woven through the platform and exportable via STIX/TAXII to SIEM, SOAR, NGFW and EDR tools.
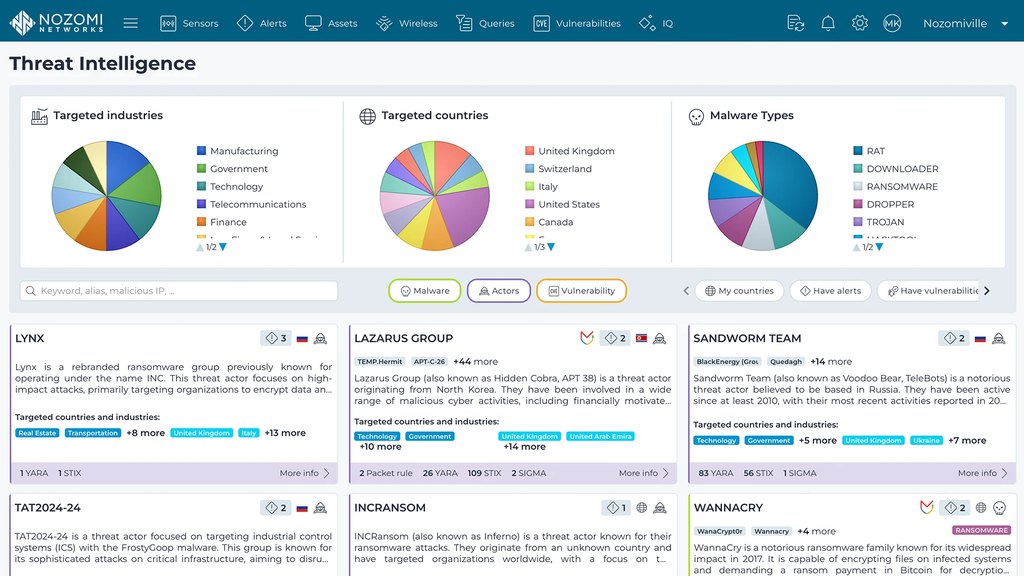
Key capabilities
- Actionable Threat Context —— Distilled threat cards with actors, exploits, malware and mitigations
- Seamless SOC Integration —— Fits existing security operations workflows and toolchains
- Cross-domain Visibility —— Unified insight into cross-domain IT/OT activity
- AI-powered Detection —— AI engine analyzes suspicious samples ahead of signatures; Mandiant expansion pack adds IOCs/TTPs