Invicti ASPM
One view of every vulnerability, deduplicated and orchestrated
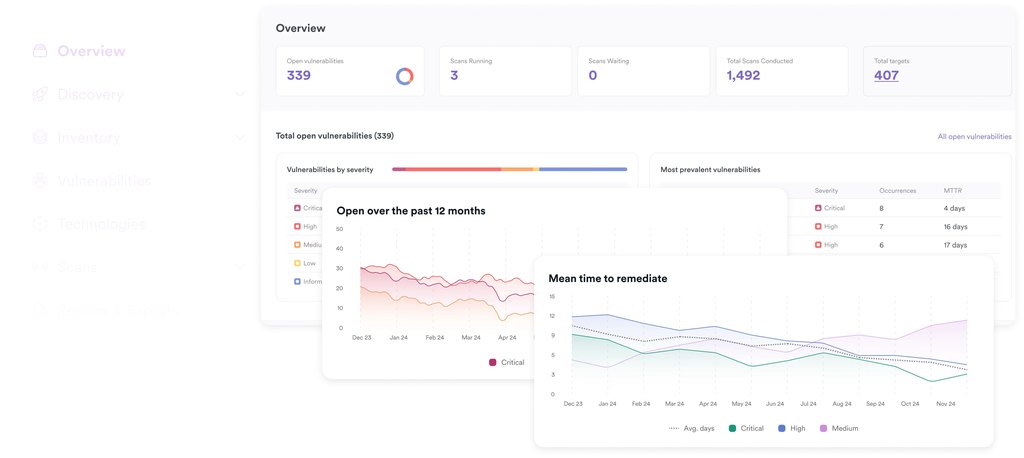
Scanners flood teams with duplicate CVEs and siloed results. Invicti ASPM unifies data across your ALM, SSO and CI/CD ecosystem, deduplicates and suppresses noise, builds hierarchical risk views and security scores by business unit or product, locates vulnerable components via SBOM, and pushes findings to Jira, Slack or GitHub with continuous remediation metrics.
Key capabilities
- Connects your ALM, SSO and CI/CD ecosystem to unify vulnerability data
- Cross-tool deduplication and suppression rules cut the noise
- Hierarchical views by business unit, product or project with risk profiling
- In-depth security scores with bulk actions across vulnerabilities
- SBOM locator: instantly find vulnerable components and impacted apps
- Sends findings to Jira, Slack or GitHub and tracks remediation KPIs