
Security Manager
Optimizing Network Security Management through Continuous Assessment
WHY SECURITY MANAGER?
Maintain continuous visibility into existing network devices and security policies.
USE SECURITY MANAGER TO:
- Optimize firewall policy rule sets.
- Map network-wide policy and access.
- Validate and report on policy compliance.
- Detect and report on policy changes.
- Ease migration to next-generation firewalls.
FEATURES:
- Traffic Flow Analysis
- Access Path Analysis
- Customizable Reporting
- PCI DSS 3.0 Assessment
- Network Map Visualization
- Advanced API Integration
Enterprise networks continue to increase in complexity, and threats to networks are more severe than ever. Protecting these environments takes more than great technology; it takes effective and continuous management. Without the right systems in place, that can be a costly and time-consuming undertaking.
FireMon Security Manager addresses the inherent complexity and changing requirements of today’s enterprise networks by providing continuous visibility into network security devices and policies.
WHAT IS SECURITY MANAGER?
FireMon Security Manager offers real-time visibility into network security infrastructure, including key indicators of device complexity, policy change and related risk. A scalable architecture and intuitive user interface ensure that security practitioners in any enterprise have the actionable data they need to quickly adapt network defenses to changing business demands and emerging threats.
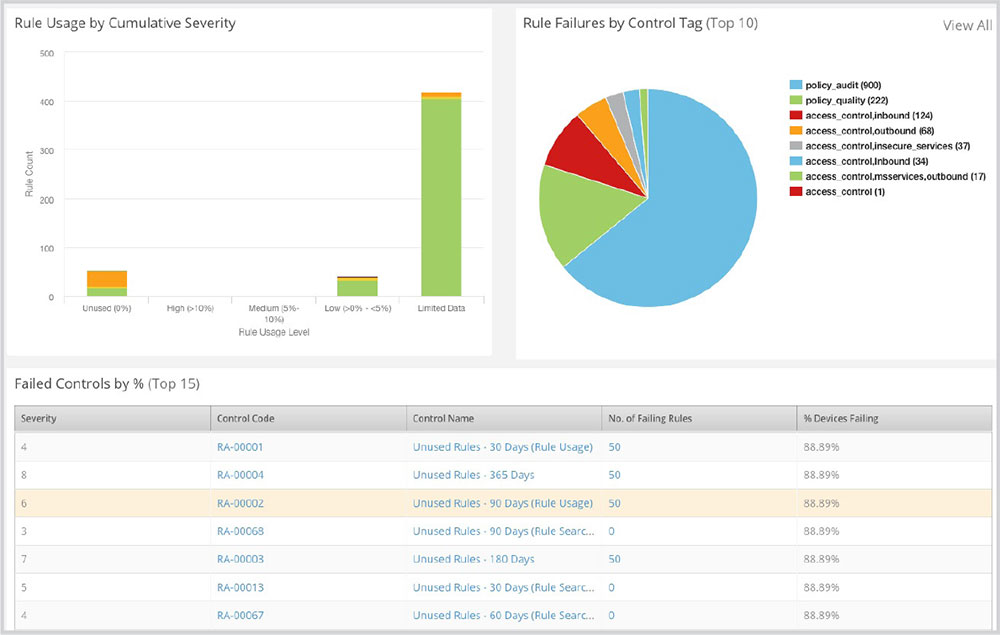
Continuous assessment of enterprise network security infrastructure.
The Security Manager platform was designed to address the three biggest challenges in firewall monitoring and management: cleanup, compliance and change.
CLEAN UP
Analyze firewall configurations to identify hidden, shadowed or overly permissive rules.
COMPLIANCE
Validate policies against regulatory requirements, including PCI DSS 3.0
CHANGE
Automate policy change workflow and scope the impact of proposed changes.
SOLUTION OVERVIEW
The core capabilities of the Security Manager platform provide detailed, customizable network security analytics and real-time assessment of policy enforcement from a single security device to the entire network infrastructure.
FIREWALL RULE ASSESSMENT & OPTIMIZATION
Track utilization, effectiveness and efficiency of every rule on every firewall to eliminate complexity and optimize performance.
AUTOMATED CHANGE MANAGEMENT
Speed up implementation and improve effectiveness of rule changes with automated change alerts, stakeholder assignment, impact analysis and full documentation.
ACCESS PATH ANALYSIS
Trace every available access path across the network and visualize relationships between network devices to identify risky access points and adjust related rules and configurations.
POLICY COMPLIANCE AUDITS
Validate firewall configurations and report on compliance for regulatory requirements, including PCI DSS 3.0, HIPAA, NERC-CIP and SOX.
NETWORK SECURITY VISUALIZATION
Maintain detailed visibility into current network security infrastructure via detailed dashboards, reports, maps and automated alerts.
NEW IN SECURITY MANAGER VERSION 8
OMNI SEARCH
Quickly search all devices, policies and rules within the enterprise from a single place in the application.
NGFW SUPPORT
Account for NGFW capabilities with application-level awareness and reverse application engineering.
DEVICE PACK SDKS
Create device packs to integrate emerging technologies directly into Security Manager.
FEATURE SPOTLIGHT
TRAFFIC FLOW ANALYSIS
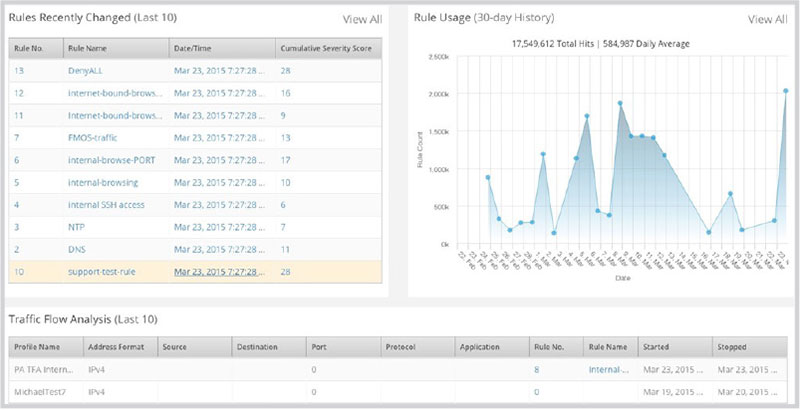
Evaluate network traffic behavior–including application-level awareness for next-generation firewalls–to isolate overly permissive configurations and reduce gaps in protection.
NETWORK MAP VISUALIZATION
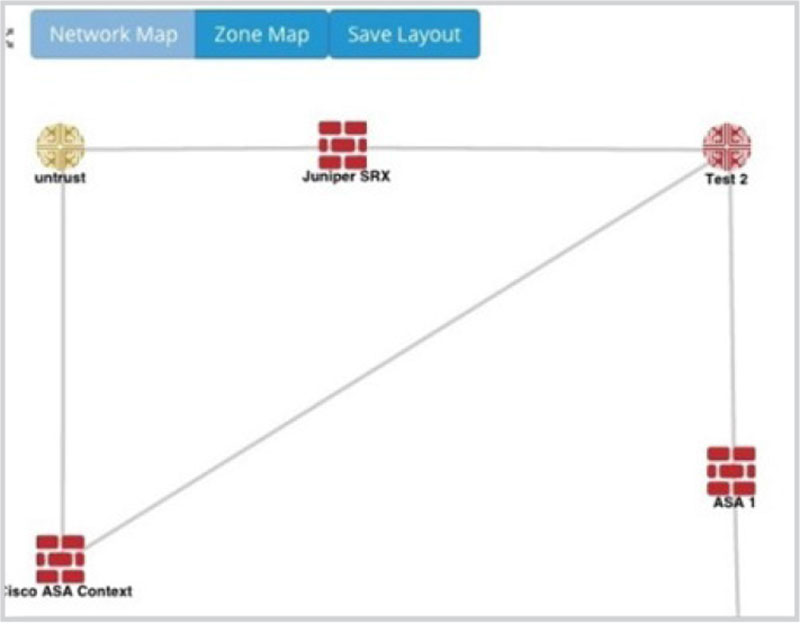
View and interact with highly complex environments or segmentations.
WEB-BASED, KPI DASHBOARDS

Customizable dashboards visualize and trend network security effectiveness, complexity and risk via key performance indicators.